Using TLS to protect data
Recommended profiles to securely configure TLS for the most common versions and scenarios, with additional guidance for managing older versions.
Recommended profiles to securely configure TLS for the most common versions and scenarios, with additional guidance for managing older versions.
The NCSC publishes its recommendations for configuring post-quantum cryptography in TLS. Now is time to migrate.
Improper restriction of XML external entity reference vulnerability (CVE-2026-88794) has been found in Sparx Systems Enterprise Architect software.
EU and NATO websites displayed online ads linked to Israeli hacking software.
CERT Polska has received a report about 3 vulnerabilities (CVE-2026-35088, CVE-2026-63314 and CVE-2026-63315) found in Slican telephone exchanges.
On 14 October 2026, Cisco published a security advisory addressing a critical vulnerability affecting the Advanced Malware Protection (AMP) feature of Cisco Secure Email Gateway. This vulnerability could allow an…
We investigated an intrusion where attackers exploited CVE-2024-47575 to target 500+ firewalls and deploy PEERSTITCH, a memory-resident ARM64 malware.
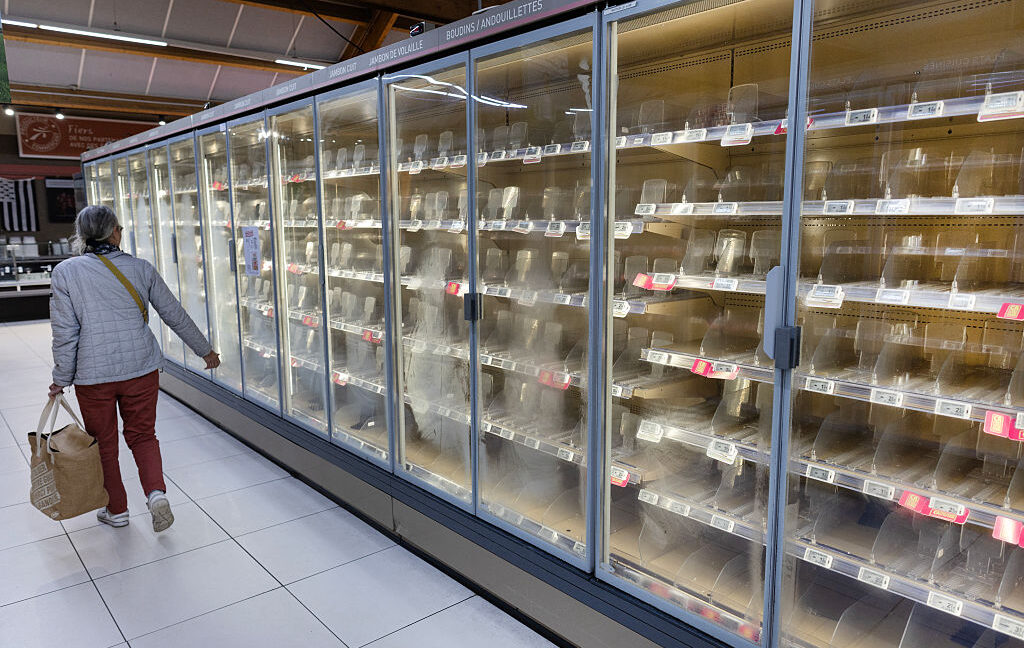
Incident hitting 700 supermarkets exploited outdated devices exposed to the Internet.
The United Kingdom has issued economic sanctions against Cryptomus, a chameleonic cryptocurrency platform that experts say serves as a major conduit for payments related to ransomware, narcotics, darknet markets, fraud…
Talos and Recorded Future identified UAT-6275 activity targeting government organizations across the Commonwealth of Independent States. Recovered artifacts show additional interest in water resources and energy.
Open Enrollment is peak season for Medicare fraud – here’s how to tell real outreach from fakes and keep your details safe
European Commission IT department wants to use AI to defend its systems from the most serious cyberattacks.
Microsoft today issued updates to fix more than 1,400 security vulnerabilities in its Windows operating systems and other software. Today's epic patch batch dwarfs September's record of nearly 1,000 fixes, which was…
Unit 42 dissects a cyberattack targeting a European bank's IT infrastructure, delivering concrete defense strategies to help organizations detect and counter comparable threats.
Microsoft has released its monthly security update for October 2026, which includes 1415 vulnerabilities affecting a range of products, including 85 that Microsoft marked as "critical."
SQL Injection vulnerability (CVE-2026-63316) has been found in Payload CMS software.
Kanishka Narayan, concerned by Australian incident, says British cyber defences could be bypassed by artificial intelligence agentUK politics live – latest updatesAn AI-driven cyber-attack similar to the OpenAI breach…
France's cyber agency coordinating with European counterparts in response to hackers.
On 12 October 2026, GitLab released versions 19.4.2, 19.3.4 and 19.2.8 of GitLab Community Edition (CE) and Enterprise Edition (EE), fixing 24 security issues among which a critical vulnerability that could allow an…
We're looking to hear from people involved in evaluating, selecting or adopting EASM.
Data breach notifications are telling victims less than ever. What the company leaves out can still shape what you do next.
Appointment or renewal reminder appears in victims’ calendar to lure them into logging in to fake Google, Microsoft or PayPal pageYou’re preparing for the week ahead and take a look at your Google calendar. There’s an…
Agents with the Federal Bureau of Investigation (FBI) on Thursday arrested the co-founder of a Canadian cybersecurity firm in connection with an investigation into the ShinyHunters hacking group that recently relieved…
Joint advisory with international partners highlights malicious targeting of organisations from a range of sectors across the globe.
Relative Path Traversal vulnerability (CVE-2026-103663) has been found in Ollama software.
ESET Research catalogs the changes of UAC-0099’s MATCHBOIL downloader from 2024 to 2026
Unit 42 details how threat actors leverage Web3 infrastructure and open-source supply chain attacks to breach enterprise cloud environments
A teenager from Amman, Jordan suspected of leading the prolific data theft and extortion group ShinyHunters has been detained and is reportedly cooperating with the FBI to identify other members of the hacking gang…
On 5 October 2026, Atlassian published a security advisory addressing a critical arbitrary file access vulnerability. It affects Bitbucket Data Center, Confluence Data Center, Jira Service Management Data Center, Jira…