Latest
US gov IT worker pleads guilty to sending Top Secret files to Ethiopia
Help desk technician agrees to minimum 10-year jail term after being caught copying files for more than 2 years
CISA Adds One Known Exploited Vulnerability to Catalog
CISA has added one new vulnerability to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2024-27834 Apple Multiple Products Improper Authentication Vulnerability This type…
CISA Confirms Hackers Exploiting WordPress Core Flaw During Software Upgrades
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a security flaw in WordPress Core to the Known Exploited Vulnerabilities (KEV) catalog, citing evidence of active exploitation. The…

ISC Stormcast For Wednesday, November 4th, 2026 https://isc.sans.edu/podcastdetail/10164, (Wed, Nov 4th)
(c) SANS Internet Storm Center. https://isc.sans.edu Creative Commons Attribution-Noncommercial 3.0 United States License.
Defense and aerospace firm settles with government over allegedly failing to meet cybersecurity contract requirements
ILC settled for $13 million, and its parent company said it resolved the issues before settling without an admission of liability.
WordPress security advisory (AV26-1117)
Serial number: AV26-1117Date: November 3, 2026 As of October 31, 2026, WordPress is affected by a vulnerability in the following product: WordPress Core Prior to 7.1.4 On November 3, 2026, Cybersecurity and…
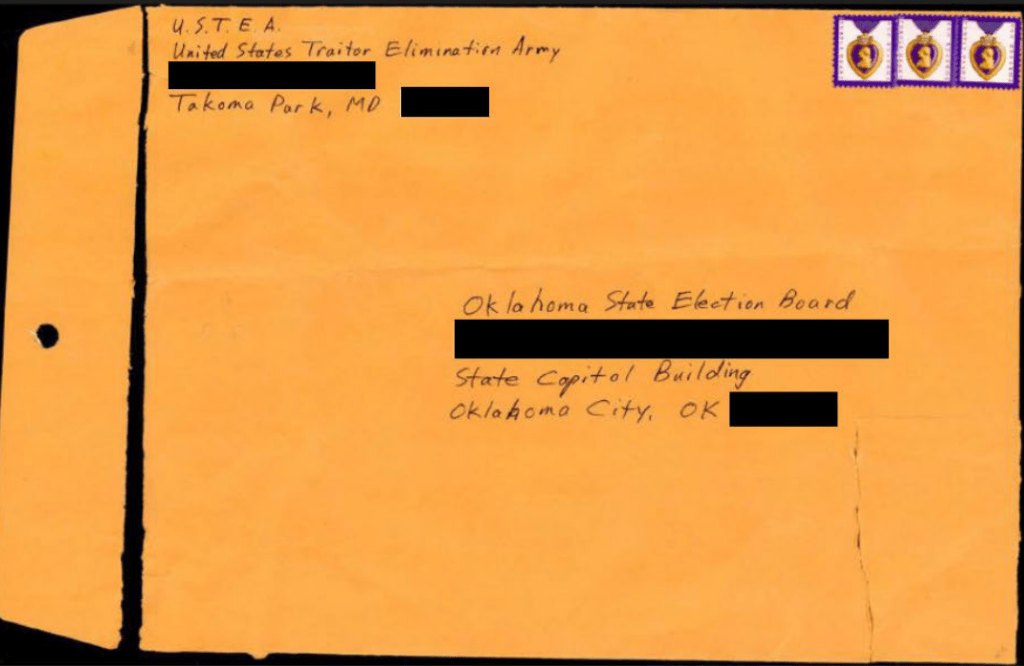
Oklahoma man charged with mailing threats, substances to election officials nationwide
Robin Patrick Martin was charged with conveying false or misleading information and hoaxes and mailing threatening communications in an effort to intimidate election officials.
Europol dismantles investment scheme that impacted potential victims in 50 countries
Authorities seized more than 100 servers and searched locations linked to the alleged operation across 17 countries.
Ballot scanner malfunctions, flurry of federal legal actions test election officials on final day of voting
Rumors of malfeasance spread on X despite no evidence, as election officials continue to fight off numerous legal challenges from the Trump administration in the last 48 hours.
CrowdStrike moves to acquire Fiddler and Dreadnode, adding AI observability and testing to its security platform
CrowdStrike is extending its platform to watch, test and explain autonomous AI agents, as enterprises face behavior-based risks that conventional security tools cannot catch.
CISA Adds One Known Exploited Vulnerability to Catalog
CISA has added one new vulnerability to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-119977 WordPress Core Time-of-check Time-of-use (TOCTOU) Race Condition…
Subnet Solutions PowerSYSTEM Center
View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to execute unauthorized SQL commands and gain access to unauthorized resources. The following versions of Subnet Solutions…
North Korea denies being behind record $6.3bn Binance hack
US government agencies and cyber analysts have blamed Pyongyang for the record-breaking heist.

As Binance reopens withdrawals, North Korea denies hacking exchange
The FBI said at the weekend that North Korea was responsible for the theft of more than $6 billion in virtual assets from Binance

ISC Stormcast For Tuesday, November 3rd, 2026 https://isc.sans.edu/podcastdetail/10162, (Tue, Nov 3rd)
(c) SANS Internet Storm Center. https://isc.sans.edu Creative Commons Attribution-Noncommercial 3.0 United States License.
FBI pins $6.3B Binance crypto heist on North Korean hackers
Exchange scrambles to replace stolen funds as customers withdraw billions and hackers get busy laundering their haul
ISC Stormcast For Monday, November 2nd, 2026 https://isc.sans.edu/podcastdetail/10160, (Mon, Nov 2nd)
(c) SANS Internet Storm Center. https://isc.sans.edu Creative Commons Attribution-Noncommercial 3.0 United States License.
FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist
The U.S. Federal Bureau of Investigation (FBI) has officially attributed the theft of more than $6 billion in virtual assets from Binance to TraderTraitor, a North Korea-aligned elite hacking group also tracked as Jade…

Chainalysis Confirms Intrusion Into Internal Tools and Exposure of Customer Identity Data
American blockchain analysis firm Chainalysis said it was the target of a cybersecurity incident in which an external actor accessed non-sensitive customer data. However, the company noted that the breach did not result…

Attackers Chain Three Ivanti Connect Secure Flaws to Gain Unauthenticated Root Access
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added two security flaws impacting Ivanti Connect Secure (ICS) to its Known Exploited Vulnerabilities (KEV) catalog, following active…

North Korean hackers linked to crypto thefts among world's best, experts say
A US State Department spokesman said North Korean cybercrime is a “global problem”

CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA has added two new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-111357 Ivanti Connect Secure Missing Authentication for Critical Function…
NCSC – CERT-SE veckobrev v.44
I veckans brev kan du läsa om att den norska nationella säkerhetsmyndigheten (NSM) höjer den nationella cyberrisknivån till hög. Du hittar även information om att sårbarheterna i PHP har lagts till i CISA:s KEV-katalog.
Suspected Chinese attackers built a custom PHP2Shell exploit and rooted 25 servers
Snoops 'likely still' have access to US government-affiliated network
Hitachi Energy CoreTec Product
View CSAF Summary Hitachi Energy is aware of OS command injection and Dirty Frag vulnerabilities that affect CoreTec product versions listed in this document. Successful exploitation of these vulnerabilities could…
CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA has added two new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-97229 GitLab Community Edition and Enterprise Edition Integer Overflow or…
Siemens Mendix SAML Module
View CSAF Summary Mendix SAML module contains an authentication bypass vulnerability that could allow an unauthenticated remote attacker to gain unauthorized access by replaying a valid SAML assertion in IdP-initiated…
Hitachi Energy TRO600 series products
View CSAF Summary Hitachi Energy is aware of multiple vulnerabilities that affect the TRO600 series product versions listed in this document. These vulnerabilities can be exploited for remote code execution (RCE) to…